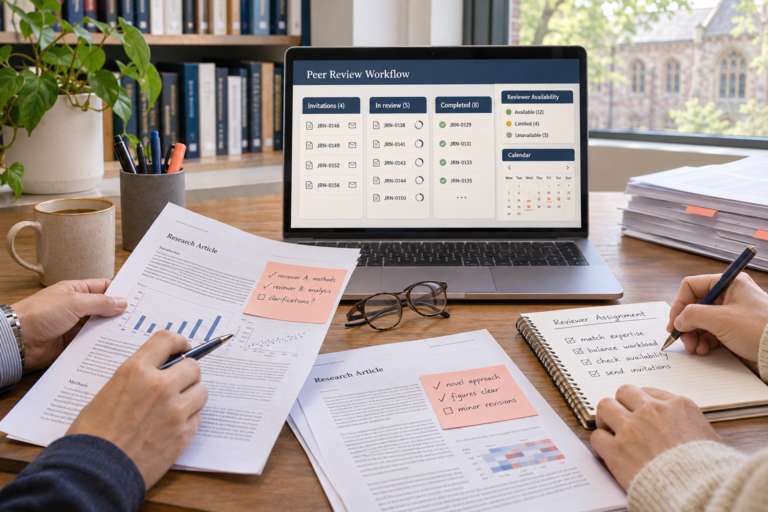
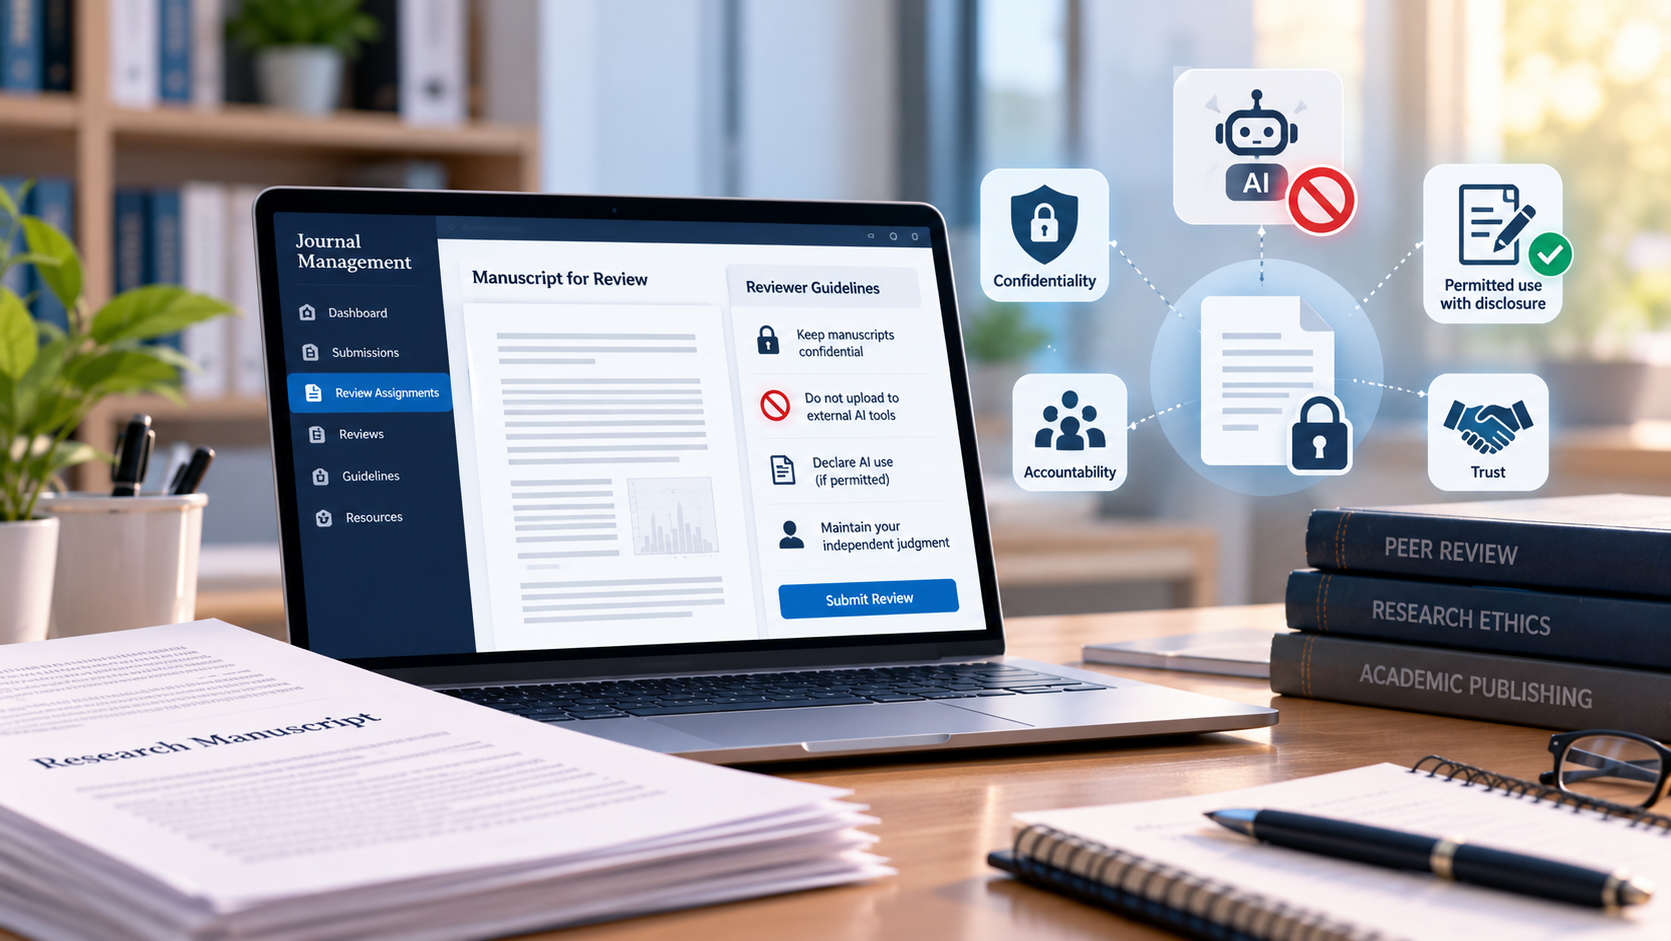
Peer review depends on trust. Authors submit unpublished research expecting that it will be shared only with people involved in editorial assessment. Reviewers accept a duty to evaluate the work carefully, protect its confidentiality and provide a report that reflects their own expertise. Generative AI complicates this process because a reviewer might use a tool to improve the wording of a report, summarize a paper or draft an assessment—actions that create different risks.
The question for journal managers is not simply whether AI is good or bad. Policies vary by publisher and journal. Many distinguish between permitted language assistance and uploading confidential manuscript content to an external AI service. Journal management platforms can help enforce these distinctions at the moment reviewers accept an invitation, access a file or submit their report.
The policy line is clearer than the software workflow
Publisher guidance gives journal teams a concrete starting point. Elsevier says reviewers should not upload submitted manuscripts or parts of them to AI tools because this may compromise confidentiality, proprietary rights or personal data; it also stresses that reviewers remain responsible for their scientific judgment. Elsevier describes limited supportive uses where confidentiality is maintained. [1]
Wiley similarly says peer reviewers must keep manuscripts and communications confidential, including by not uploading manuscript content to generative AI tools. Its policy requires transparent declaration when such tools are used to improve a review report. [2] Nature also publishes policies for referees, and reviewers must check the applicable journal guidance before using tools. These examples should not be treated as one universal rule: a multi-publisher platform needs configurable policies and must direct reviewers to the current instructions for each journal. [3]
Make confidentiality a platform behavior
A policy page can explain the rule, but the platform should make the safe choice practical. Show a short, journal-specific notice when a reviewer accepts an assignment and again before opening the manuscript or submitting a report. The notice should explain what is prohibited, which supportive uses may be permitted, what must be disclosed and whom to contact when guidance is unclear.
Protect access through role-based permissions and secure file handling. Only assigned reviewers and authorized editors should access the manuscript; downloaded files and supplementary data should be handled under the same confidentiality expectations.
Logs should record access, downloads, role changes and relevant disclosure steps. Where feasible, watermark files or apply controlled access links, but do not mistake watermarks for a substitute for permissions and auditability.
AI functionality built directly into the platform needs its own review. Administrators should know what content is sent to a service, where it is processed, whether inputs are retained, whether they can be used for model training, and which parties can access the result. A button labelled “Summarize manuscript” beside a confidential submission may imply that the action is allowed even when policy forbids it. Hide or disable functions that conflict with the journal’s rules.
Turn policy into a contextual workflow
For publishers managing many journals, keep a versioned policy record with an owner, effective date, journal scope and approval history. When a rule changes, the platform should show the right version to new and active reviewers and retain evidence of acknowledgment. This is more reliable than copying policy text into separate journal pages that may drift out of date.
Disclosure questions should be proportionate and specific. The platform might ask whether an AI tool was used, for what purpose, which service was involved and whether any confidential manuscript content was entered. A reviewer who used a permitted tool for grammar correction should not face the same workflow as one who shared an unpublished paper with an unapproved external service. Answers can be routed to an editor for review rather than treated as automatic proof of misconduct.
Keep the human reviewer accountable
Peer review is an expert judgment, not a text-generation exercise. AI can help organize a reviewer’s own notes, but it can also produce fabricated references, miss methodological flaws, misunderstand a specialized method or state an unsupported conclusion confidently. A polished report is not necessarily a reliable report.
The named reviewer should inspect and approve the final assessment. The platform can ask reviewers to confirm that the scientific analysis reflects their own evaluation, that sources and factual claims have been checked, and that any required AI use has been disclosed. Editors should be able to query unclear reports and assess the substance of the review rather than relying only on writing style.
Automated AI detectors are not conclusive evidence of authorship or misconduct. False positives and negatives occur, and a detector cannot judge scientific validity. Treat potential signals—missing disclosure, unusual access, fabricated references or a report that ignores the methods—as prompts for proportionate human review, not an automatic penalty.
Practical example: a reviewer wants help with wording
Imagine a reviewer has completed a careful technical assessment but wants to improve the clarity of the report. The journal allows grammar assistance but forbids uploading manuscript text to outside tools. This is an illustrative scenario. A general-purpose “Improve with AI” button that sends the manuscript and report to a third party could breach the policy even if the reviewer intended only to polish the prose.
A better platform design offers a clearly approved workflow that processes only the reviewer’s own draft report, and only through a service whose data handling has been assessed. Before use, the platform states the limitation; after use, the reviewer checks the revised report and completes the required disclosure. If no approved service exists, the feature stays disabled. The reviewer remains responsible for every scientific claim submitted to the editor.
A safer implementation checklist
Before launching an AI feature, confirm that policy permits the use, define what content leaves the platform, assess the service’s data handling, specify disclosure and logging, and name the person responsible for reviewing outputs. If anything is unclear, keep it disabled.
For multi-journal publishers, track policy coverage, acknowledgments, disclosure completion, access exceptions and unresolved concerns. Keep logs proportionate; they should support security and governance without collecting unnecessary personal information. Review configurations whenever policies, vendors or journal requirements change.
No platform or policy can eliminate every risk. Journal systems can reduce accidental breaches by presenting instructions in context, blocking unapproved data flows, recording meaningful events and keeping editorial responsibility with humans. The goal is to protect peer review while making permitted workflows easier to follow.
Sources cited and further reading
1. Elsevier, “Generative AI policies for journals” ↩